6 Cyber Security Supply Chain Risks & Challenges
Cyber security measures have had to ramp up, especially with the increase of businesses and organisations relying on third-party suppliers, vendors and MSPs as part of their supply chain. This has led to a rise in supply chain attacks, where these third-party tools and services become entry points for attackers, leading to eventual malware being delivered to the ultimate target. At Optimising IT, we specialise in keeping businesses secure. Here are six cyber security supply chain risks to be aware of and how to manage them effectively. What Is Supply Chain Cyber Security Risk? A supply chain in the context…

Cyber security measures have had to ramp up, especially with the increase of businesses and organisations relying on third-party suppliers, vendors and MSPs as part of their supply chain.
This has led to a rise in supply chain attacks, where these third-party tools and services become entry points for attackers, leading to eventual malware being delivered to the ultimate target.
At Optimising IT, we specialise in keeping businesses secure. Here are six cyber security supply chain risks to be aware of and how to manage them effectively.
What Is Supply Chain Cyber Security Risk?
A supply chain in the context of cyber security involves the potential vulnerabilities and threats that arise from the interconnected network of external partners, vendors and service providers that an organisation relies on. Modern developments have seen the “supply chain” extend beyond physical goods to include software, data services, cloud infrastructure and third-party integrations.
Security risks can exist at any point in the supply chain, whether it’s a compromised software update from a vendor, insecure APIs or weak access controls in a partner system. Even if a business maintains strong internal defences, vulnerabilities in third-party software and tools can be exploited to gain indirect access.
Businesses and organisations are seeing more threats and finding it challenging to manage risks because of the lack of control over third-party tools. The consistency in protection across the entire supply chain is turbulent, as businesses can’t enforce their own security policies on vendors. This reliance on external software and systems requires careful risk management and continuous monitoring to reduce exposure to supply chain attacks.

6 Cyber Security Risks and Challenges in Supply Chain
1. Third-Party Vulnerabilities
One of the most significant supply chain cyber security risks to understand is the vulnerabilities of third-party vendors. Suppliers often have varying levels of security in place, and those with weaker controls can become easy entry points for attackers. Often, vendors are connected to multiple organisations and a single compromised supplier can create a ripple effect, impacting many different businesses at once. It’s crucial to understand and assess the level of security your third-party vendors have to help you manage supply chain risks.
2. Ransomware Attacks
Another huge risk is ransomware attacks, which have become increasingly common across supply chains, targeting both large organisations and smaller suppliers. Attackers will exploit the weakest link in the supply chain to gain access and deploy ransomware more broadly. Cybercrime groups are using ransomware-as-a-service (RaaS) more and more, because it is making attacks more accessible, and lowers the barrier of entry for attackers. It mirrors legitimate software-as-a-service (SaaS), giving subscribed attackers access to malicious code created by operators as part of the service, and then selecting the targets and deploying the malware.
3. AI-Driven And Social Engineering Attacks
AI and social engineering tactics such as phishing, impersonation and fraud is a huge risk to businesses. These tools used by attackers allow for highly personalised and convincing attacks at scale, making them harder to detect.
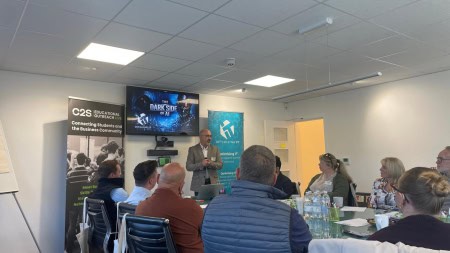
Our own Todd Gifford recently spoke at the Data & Cyber Security conference about the dangers of this type of cyber threat. He spoke about the dark side of AI, and how cyber criminals are exploiting users’ trust with seemingly normal advice from AI platforms like ChatGPT and Grok, with the advice often leading to a user entering a command which implements malware.
Other AI risks involve deepfake audio and video, where attackers can impersonate as third-party suppliers to deploy phishing and malware attacks. Todd also touched on the ethics of using the technology, using real-world examples of how businesses have had to strengthen cyber security to better manage AI risks and threats.
4. IoT and connected device vulnerabilities
The Internet of Things (IoT) is used by the entire supply chain for things like tracking shipments, ensuring visibility and efficient connectivity. The rapid growth of connected devices across supply chains has introduced new challenges. Many IoT devices and their associated APIs lack strong security controls, making them attractive targets for attackers. These include weak authentication, unpatched firmware and device-level vulnerabilities, all of which can be exploited to gain access to wider networks.
5. Lack of visibility and control
A common challenge in supply chain cyber security is limited visibility to the security practices of suppliers and partners. Organisations often struggle to assess the true security posture of third parties or to monitor risks in real time. This lack of transparency makes it difficult to identify vulnerabilities, enforce standards or respond quickly to emerging threats across the full supply chain.
6. Geopolitical and external threats
Supply chains are increasingly affected by geopolitical tensions and external threats. This has led to the UN implementing new cyber security measures for not just businesses, but nations as a whole. This is because state-sponsored attacks are putting supply chains at risk, with global instability putting businesses in the middle of the conflict. These conflicts are things like trade disputes and economic sanctions, which increase cyber risks by creating uncertainty, weakening oversight and exposing critical dependencies within the supply chain.

The Role Of Standards and Certifications
If you’re looking to improve your cyber security supply chain risk management, you’ll need to understand the different standards and certifications that can strengthen your supply chain security.
These standards and certifications provide a consistent framework that organisations and their third-party suppliers can follow. One widely recognised standard is Cyber Essentials, which focuses on fundamental security controls such as secure configuration, access control, malware protection and patch management. Adopting this framework helps businesses defend against common cyber threats and creates a shared standard that suppliers can align with.
To ensure credibility, certification is verified through an independent Cyber Essentials Certification Body. Optimising IT is an IASME-approved Cyber Essentials Certification Body, and can assess a business’s security measures and support you in gaining the right security measures and obtaining certification.
Read more on the latest 2026 changes for Cyber Security Essentials here.
Ultimately, recognised standards and certifications help build trust with partners and customers. They demonstrate a commitment to cyber security, reduce exposure to common threats and support more secure collaboration across the supply chain.
Protect Your Business From Supply Chain Cyber Threats
Supply chain cyber risk is no longer just an IT concern, it’s a business-critical issue that can impact operations, reputation and revenue. This means going beyond one-time assessments and implementing ongoing monitoring, regular audits and continuous support.
Work with Optimising IT for expert managed IT support and to help assess and manage risks, implement effective controls and maintain a resilient cyber security posture across your entire supply chain.

Book a Meeting
Run, Protect
and Grow, Your Business

Company News